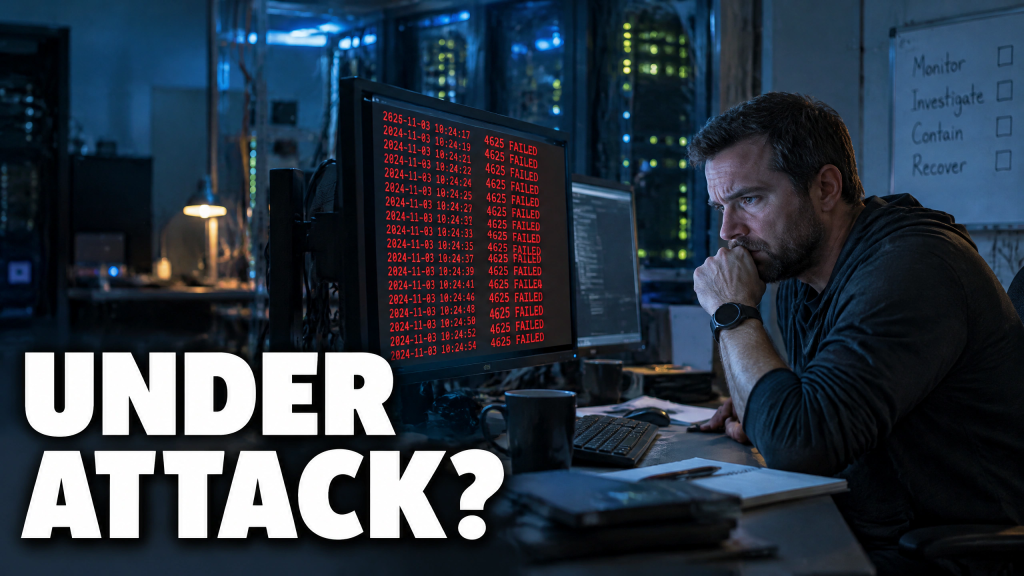
A screen full of failed logins quickly grabs attention. The count climbs, the source looks unusual, and everyone wants an answer: are we under attack? Windows Event ID 4625 records a failed logon. It does not establish a breach. Repeated failures may indicate an attack, outdated service credentials or an authentication misconfiguration. The details determine what to investigate.
What Windows Event ID 4625 Reveals
Microsoft documents the event as a failed logon generated on the computer where the attempt was made. Its fields can include the account name, logon type, workstation, source network address and failure status. Field availability varies with the authentication context.
Those details matter more than the count. A few failures against a privileged account from an unfamiliar address may require a different response than thousands of attempts from an internal service using a deleted username.
Substatus 0xC0000064 identifies a bad or misspelled user account. It is a useful starting point, but it does not explain why that identity was submitted.
A scheduled task, service or script may still reference an account that was renamed or removed. An attacker may also be testing usernames. Investigate the source before deciding which explanation fits.
Investigate Internal Sources and SSO Failures
An internal IP address does not establish that the activity is safe. A firewall, proxy, remote-access gateway or identity service may be acting on behalf of another system.
Start with the source’s normal role. Does it handle single sign-on (SSO), query Active Directory or collect user-session information? WatchGuard’s documentation describes SSO components that obtain user information through clients and event logs. That makes the supporting authentication services relevant to an investigation; it does not prove that WatchGuard caused a particular failed-login pattern.
Compare the failures with normal activity. Attempts at fixed intervals may suggest a scheduled process. Bursts around user sign-ins may warrant checking the SSO integration. Failures across many accounts may warrant investigating password spraying or automated username discovery.
Use the logon type to help distinguish interactive, network, service and remote interactive attempts. Treat each pattern as a lead to test.
Check Successful Logins and Account Changes
Windows Event ID 4624 records a successful logon. Search for successes involving the same account, source and target around the time of the failures. Where populated and applicable, logon IDs and GUIDs can help connect successful sessions with related events.
“No successful logins observed” is useful evidence only if the relevant systems, audit settings and time period are covered.
Review account creation, privilege and group changes, remote-access sessions, service installations and unusual outbound connections. Confirm whether the failed username exists in the relevant domain and whether it was recently deleted or renamed.
Then inspect the source component’s service account, stored credentials, SSO settings and recent changes. Nobody may have edited the firewall, yet a password rotation, software update, restored backup or directory change could have affected its authentication dependencies.
Fix the Authentication Misconfiguration and Verify
If the evidence supports a configuration issue, correct the specific fault. Suppressing the alert or excluding a noisy source leaves the cause unresolved.
Monitor through the affected process’s normal operating cycle to confirm that the failures stop. Keep the before-and-after logs and document the cause, the correction and the checks for unauthorized access.
If suspicious activity continues, spreads to other accounts or includes unexpected successful access, escalate the investigation. Preserve logs and, where practical, contain the source.
A credible explanation begins a finding. Close the alert when evidence supports the cause and you’ve verified the correction.
The businesses that benefit most are the ones that take the time to get their systems right first. Schedule a performance review on how to defend hiring a hacker at www.CybersecurityMadeEasy.com to assess your AI readiness and strengthen your operational foundation before you start building on top of it.
Stay informed, protected, and one step ahead of fraudsters with Fraudster, the ultimate mobile app. Download now to receive real-time push notifications, stay updated on the latest frauds and scams, and get valuable tips to protect yourself. Available for iOS and Android, Fraudster is your trusted ally in the fight against fraud. Don’t wait! Visit http://www.FraudsterApp.com to learn more about our mission and start securing your digital world for free.


